Mobile App Security in the Age of AI: Why We Now Need to Dig Much Deeper
Many companies know pretty well which apps are in use within their environment. However, the much more intriguing question these days is: What software is actually behind these apps, and where does AI come into play? We explain what has changed as a result of AI and how mobile endpoint security must be structured today. Modern cybersecurity is based on two crucial factors: strong technical protection that goes deeper than ever before, and proper human intervention. In this article, we’ll explore what this means for companies in concrete terms.

What is mobile app security today?
Modern mobile applications have long since ceased to consist solely of code from a single vendor. They contain open-source components, software development kits, embedded libraries, interfaces, and third-party services. This is normal. It makes apps powerful, quick to develop, and flexible. At the same time, however, this creates a new attack surface that many companies barely notice.
The integration of AI components, in particular, requires a shift in perspective: mobile security is evolving from pure threat detection to mobile exposure management. In other words, it’s about identifying the risks present in mobile applications before they escalate into an active security incident.
However, a simple list of installed apps reveals nothing about what data they send or where, nor whether they use AI models in the background that process sensitive information. This is precisely where the actual attack surface lies.
Anyone who views mobile security today solely through the lens of device and app inventories is missing the bigger picture. What matters most today is transparency regarding software components, data flows, and AI usage on mobile endpoints. Only when these aspects are visible can mobile security be truly effective.
AI shortens the response time for attackers
The threat landscape is changing not only because there are many hidden entry points within applications, but also because attacks are becoming faster.
Whereas it used to take days or weeks between the disclosure of a vulnerability and its potential exploitation, AI systems now turn vulnerable components into a real risk very quickly.
This is changing the work of security teams. It is no longer enough to search for known malicious apps or obvious indicators of malware. Companies must understand which components are contained in legitimately used apps and whether these components contain known vulnerabilities. The risk may lie in an outdated library, a vulnerable SDK, or a software dependency.
From app inventory to Mobile Exposure Management
A traditional app inventory shows you which apps are installed and which versions are in use. However, it does not automatically reveal which software components are used within those apps.
This difference is more than just semantic. While an app inventory lists the existing apps, Mobile Exposure Management assesses the risk. And that’s becoming increasingly important in the mobile context.
Modern Work isn’t just about enabling people to work productively. Modern Work must also remain secure, manageable, and traceable—especially when work is mobile, hybrid, and AI-supported.
Uncovering the blind spot in the mobile software supply chain
An approach is needed to analyze mobile applications at the component level. This involves examining app binaries, software bills of materials, known vulnerabilities, affected apps, users, and devices. This is relevant for businesses because many mobile apps consist of numerous embedded components. A vulnerability in a shared library can thus extend across multiple seemingly harmless apps. Without transparency, it remains unclear which teams, devices, or roles are actually affected.
Visibility determines whether a risk can be prioritized and specifically mitigated, or whether it remains unnoticed in the background. The first solutions for this already exist, and we’ll introduce them to you in this blog post.
AI Visibility & Governance: The second strategic building block
Linked to this is a second issue that many companies are currently grappling with: the use of AI outside of clear governance structures.
Employees are increasingly using AI tools in their day-to-day work. This is understandable, often productive, and represents real progress in many scenarios. At the same time, the question arises as to whether companies have sufficient visibility into which AI applications are being used, what data is flowing to them, and what policies apply.
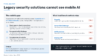
This is precisely where Mobile Exposure Management and AI Visibility & Governance intersect. Thanks to AI, mobile devices have become a source of AI risks, data privacy concerns, and compliance requirements. This is because traditional firewalls, CASB, and secure web gateway solutions fail to detect many mobile AI activities, as communication often takes place directly between the app and the cloud service. This creates blind spots in existing security architectures.
Transparency is therefore essential for mobile software components as well as for shadow AI, app-to-cloud data flows, and the use of external AI services. With transparency, companies can assess, prioritize, and establish appropriate guidelines.
What companies should be reviewing now
This raises specific audit questions for IT, security, and compliance teams.
App transparency
Do you know not only which apps are installed, but also what components they contain?
Risk assessment
Can you identify which apps pose risks due to known vulnerabilities in SDKs or libraries?
Risk prioritization
Can you prioritize risks based on actual exposure, affected users, and business relevance?
AI Usage
Can you see which AI services and AI-enabled apps are actually being used on mobile devices?
Governance
Are there clear guidelines regarding the use of AI on mobile devices, data protection, and permissions?
System integration
Can your policies be implemented in UEM systems and security processes?


Why this is not purely a security issue
Mobile Exposure Management is not just a technical add-on. It is a strategic issue for Modern Work.
After all, modern workplaces thrive on people being able to work productively on any device—in the office, at home, or on the go; on iOS, Android, Windows, or macOS. This freedom requires security that keeps pace with the realities of work.
When mobile devices combine identity, access, communication, files, and AI-powered work into a single interface, the IT team must be able to identify the associated risks. Not to stifle innovation, but to enable it responsibly and sustainably over the long term.
Conclusion: Modern mobile app security starts beneath the surface
Risks in app ecosystems often remain hidden: Modern mobile apps consist largely of third-party code. Not only the app itself, but also hundreds of integrated libraries, SDKs, and third-party APIs harbor latent security vulnerabilities. This is precisely where greater transparency and concrete risk assessment are needed.
Our partner Lookout has been successful in mobile threat defense for several years. In 2016, they and the Citizen Lab discovered the Pegasus spyware, and more recently, for example, they uncovered the DarkSword exploit chain.
With the Mobile Software Exposure Center (MSEC), they are now showing where the market is headed: away from mere app visibility, toward deeper exposure intelligence on mobile endpoints. Combined with AI Visibility & Governance, this provides a more comprehensive view of mobile risks, software supply chains, and the use of AI services. This provides organizations with the transparency they need to make informed security, compliance, and governance decisions.
- Visibility through SBOM (Software Bill of Materials): Lookout’s MSEC analyzes mobile applications down to the component level. Customers receive a detailed SBOM of their mobile fleet and can see exactly which libraries, SDKs, and other software components are included—and what risks they pose.
- Assessment via MTTP (Mean Time to Patch): A key indicator of an app’s risk is the developer’s response time. MSEC evaluates the Mean Time to Patch (MTTP) of app providers. This reveals which apps pose a persistent security risk because known vulnerabilities are not addressed promptly.
- AI Visibility & Governance: Companies gain visibility into which AI applications are being used on mobile devices, what data flows are generated to AI services, and where shadow AI risks may arise. To this end, Lookout focuses on identifying and classifying AI applications, analyzing data flows and app behavior, and enforcing governance and security policies for AI usage.
Contact us
Would you like to know how visible mobile risks, AI usage, and app exposures really are in your environment? EBF helps you evaluate your modern work, UEM, and security strategies and develop concrete guidelines based on those assessments.